ACM Foil
ACM Foil is inspired by Greg Procunier's (gprocunier) Blastwall project. Blastwall demonstrates hardened fleet management for RHEL with IdM, with a path for bringing that same hardened disposition to OpenShift workloads. ACM Foil extends that model into ACM-driven OpenShift fleet management.
Use ACM Foil when you want GitOps and ACM to deliver stricter workload confinement, controlled cluster placement, and compliance evidence across selected OpenShift clusters. See Blastwall Workload Confinement for the benefits and adoption boundary.
Quick Start
- Deploy
- Target a cluster
- Validate
oc apply -f apps/hub/argocd-application.yaml
oc label managedcluster <cluster-name> spo=true --overwrite
oc get applications.argoproj.io -n openshift-gitops spo-acm-policies-test
oc get policy,policyset,placement,placementbinding -n acm-spo-policies
Current Policy Flow
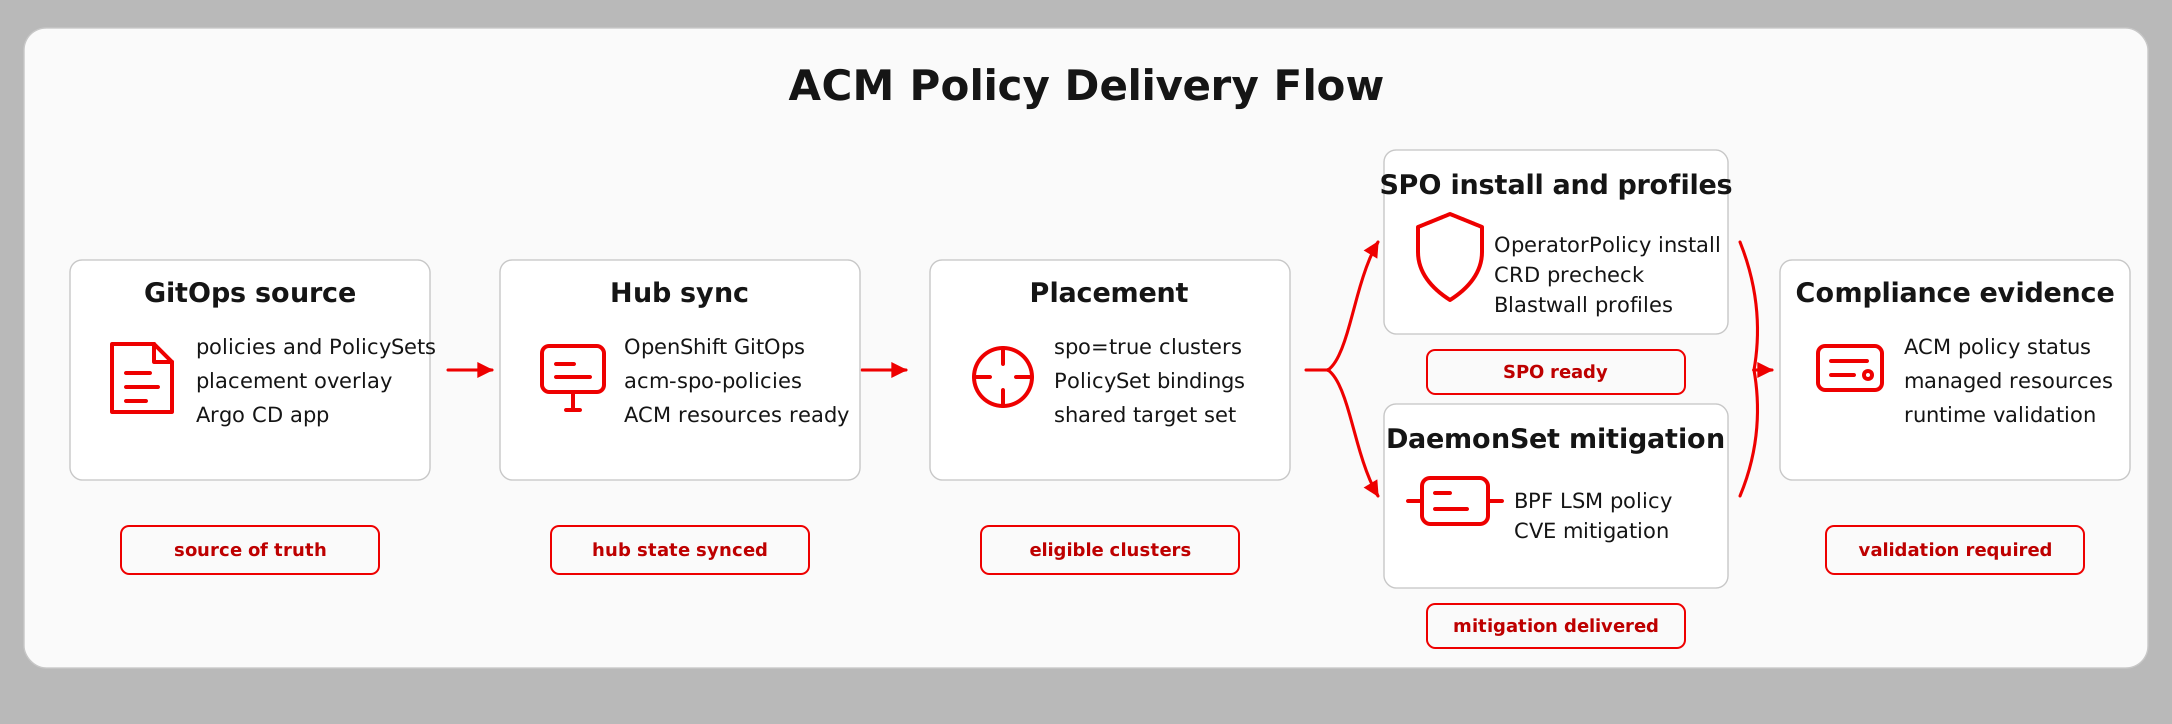
What It Deploys
| PolicySet | Purpose |
|---|---|
policyset-blastwall-test | Deploys Blastwall SPO profiles, waits for status.usage, and applies status-derived SCC/RBAC bindings. |
policyset-spo-test | Installs the Security Profiles Operator and deploys a Red Hat CVE mitigation policy. |
ACM Foil installs the Security Profiles Operator on selected managed clusters through ACM OperatorPolicy. Clusters must have OLM and access to the Red Hat operator catalog.